What Are AI SOC Agents and How They Work
Introduction
Security Operations Centers face relentless pressure today. Alert volumes are rising exponentially, skilled analysts are in short supply, and threat actors are accelerating the pace and sophistication of attacks. According to multiple industry studies, large enterprises now process tens of thousands of security alerts per day, while mid-sized organizations routinely handle thousands.
IBM's Cost of a Data Breach Report consistently shows that the average time to identify and contain a breach exceeds 270 days, with security operations efficiency being one of the strongest factors influencing breach cost and impact.
Traditional SOC models struggle to keep up because they rely heavily on manual investigation workflows and fragmented tooling. In response, a new category of capability has emerged: AI SOC agents. These autonomous systems are designed to investigate alerts, correlate data across security tools, and deliver decision-ready insights at machine speed.
This article explains what AI SOC agents are, why they matter, how they work, and how they differ from traditional SOC tools. It is intended as an educational resource for security leaders, SOC managers, and practitioners evaluating the future of security operations.
What Is an AI SOC Agent
An AI SOC agent is an autonomous software entity that performs tasks traditionally handled by human security analysts within a Security Operations Center.
Unlike static rules or signature-based systems, AI SOC agents use machine learning, probabilistic reasoning, and contextual analysis to evaluate security signals. These agents can investigate alerts, enrich them with contextual data, correlate activity across multiple sources, and assess the likelihood that an event represents a real threat.
Gartner and other industry analysts increasingly describe this shift as agentic security operations, where intelligent systems act independently within defined guardrails to support human analysts.
Why AI SOC Agents Matter Now
Key statistics driving the need for AI-powered security operations
Days to Contain
Average time to identify and contain a security breach
False Positives
SOC teams report majority of alerts are false positives
Talent Gap
Unfilled cybersecurity roles worldwide according to (ISC)²
Attack Speed
Time from initial access to lateral movement in modern attacks
Persistent Alert Overload
Alert volume has become one of the most significant challenges in modern SOCs. According to research published by the SANS Institute, more than 60 percent of SOC teams report that the majority of alerts they investigate are false positives.
Additional studies show that:
- SOC analysts spend over half of their time triaging low-value alerts
- Alert fatigue contributes directly to missed incidents and analyst burnout
AI SOC agents address this by suppressing low-confidence noise, correlating related signals, and prioritizing alerts based on context and inferred risk rather than isolated indicators.
The Cybersecurity Talent Gap
The global shortage of cybersecurity professionals continues to widen. (ISC)² reports a workforce gap of over 4 million unfilled cybersecurity roles worldwide, with SOC analyst positions among the hardest to fill.
This shortage creates operational risk:
- Teams are understaffed
- Analysts are overworked
- Turnover rates increase
AI SOC agents help offset this gap by automating repetitive investigation tasks and standardizing analysis quality across incidents.
Faster and More Automated Threat Actors
Threat actors increasingly use automation, living-off-the-land techniques, and credential abuse to evade detection. According to Mandiant and CrowdStrike reporting, many modern attacks now progress from initial access to lateral movement in under one hour.
Manual SOC workflows are not designed for this pace. AI SOC agents operate continuously and at machine speed, enabling earlier detection and faster response.
How AI SOC Agents Work
The investigation lifecycle that mirrors and augments human SOC workflows
Data Ingestion & Normalization
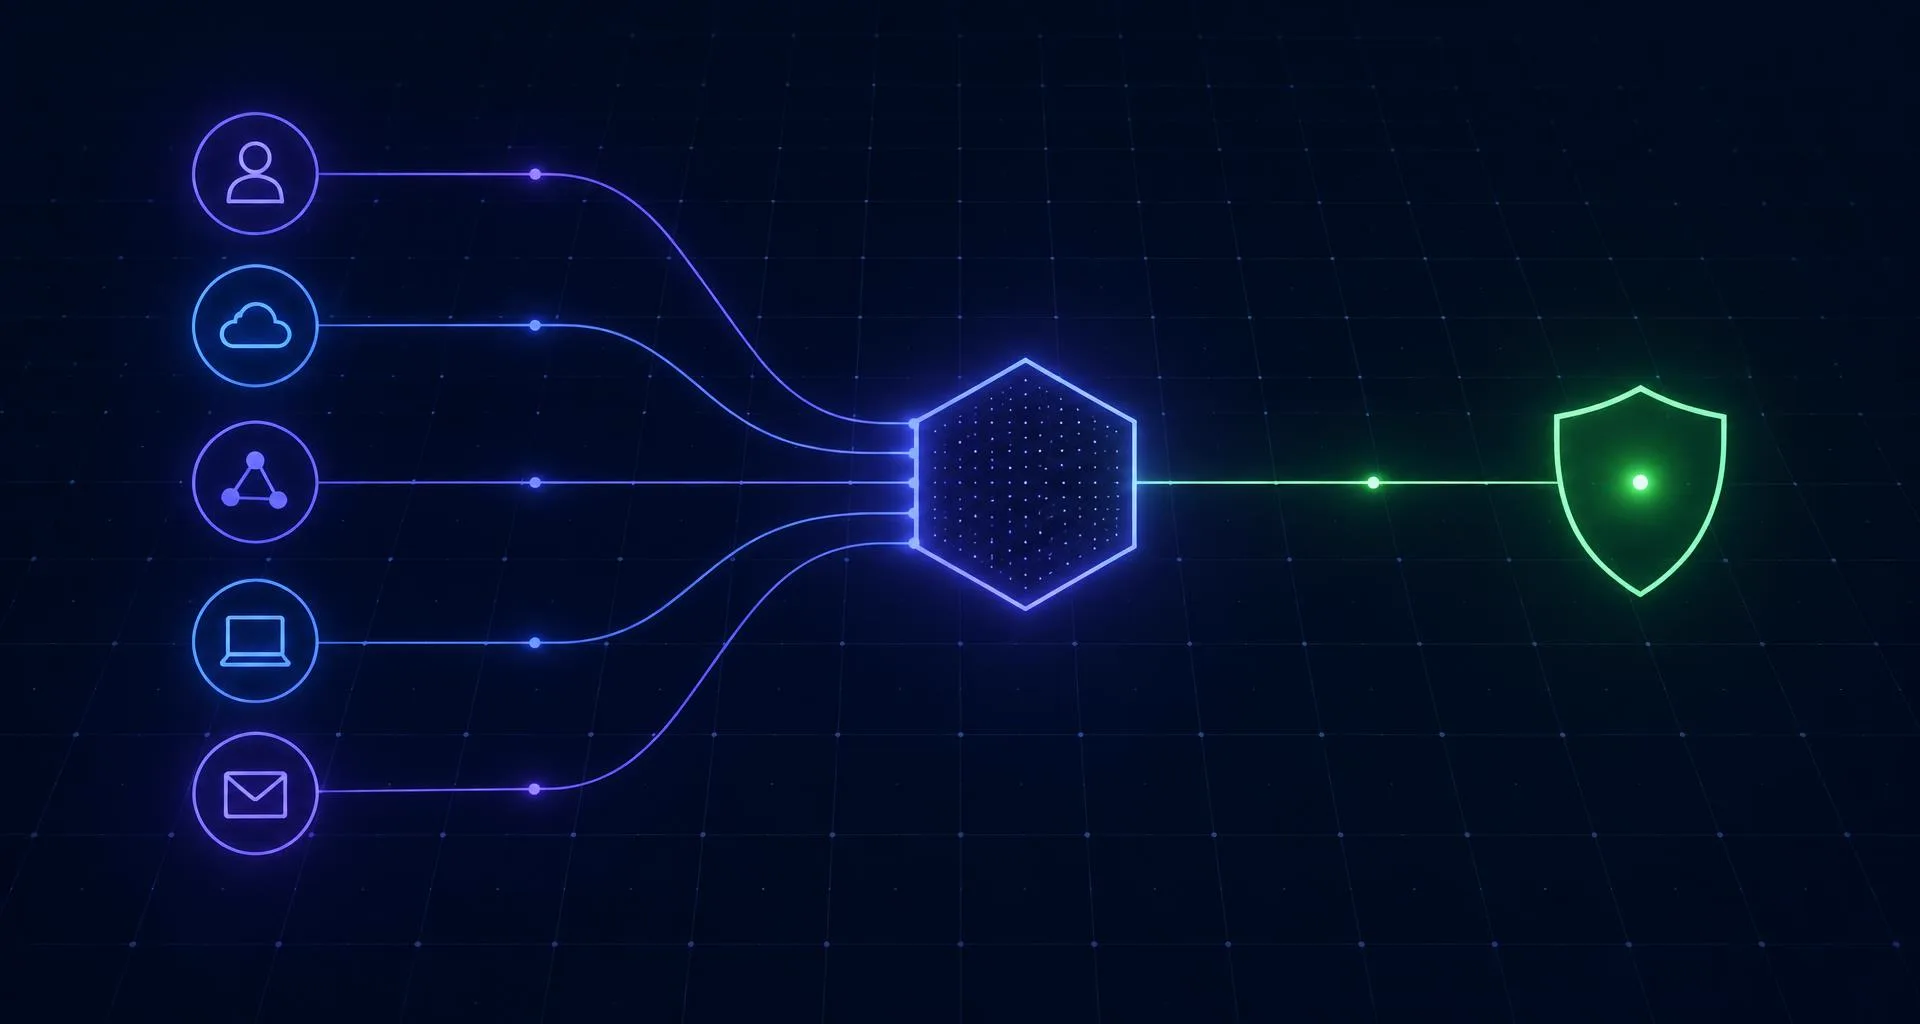
Ingest data from SIEM, EDR, network flows, identity providers, cloud platforms, and threat intel feeds
Contextual Correlation
Correlate activity across time, users, systems, and behaviors to identify multi-stage attack patterns
Intelligent Investigation
Reasoning engine evaluates evidence, weighs indicators, and computes confidence scores
Prioritization & Triage
Rank alerts by risk, confidence, and impact. Suppress noise, escalate real threats
Actionable Output & Response
Deliver decision-ready alerts with context, evidence, and recommended response actions
Data Ingestion and Normalization
AI SOC agents ingest data from across the security stack, including SIEM logs, endpoint telemetry, network flows, identity providers, cloud platforms, and threat intelligence feeds.
Large enterprises often aggregate terabytes of security telemetry per day. Normalization enables agents to reason across heterogeneous data sources without requiring manual parsing.
Contextual Correlation
Rather than evaluating events independently, AI SOC agents correlate activity across time, users, systems, and behaviors. This allows them to identify attack patterns that span multiple tools and stages.
Industry research shows that attacks involving multiple stages and tools are significantly more likely to evade detection when events are analyzed in isolation.
Intelligent Investigation
At the core of an AI SOC agent is a reasoning engine that evaluates evidence, weighs indicators, computes confidence scores, and synthesizes findings into a coherent narrative.
This mirrors the process used by experienced analysts, but operates continuously and without fatigue. Some AI-driven SOC platforms report reducing initial investigation time from hours to minutes for common alert types.
Prioritization and Triage
AI SOC agents rank alerts based on risk, confidence, and potential impact. Low-risk alerts are deprioritized or suppressed, while high-confidence threats are escalated with supporting evidence.
Organizations that implement intelligent prioritization frequently report 30 to 70 percent reductions in alert volume, depending on environment maturity and signal quality.
Actionable Output and Response
The output of an AI SOC agent is a decision-ready alert that includes investigation context, evidence, and recommended actions. In environments with automated response enabled, agents may initiate containment actions such as account suspension or endpoint isolation.
According to multiple SOC maturity studies, organizations that automate portions of response see material reductions in Mean Time to Respond, often exceeding 40 percent.
AI SOC Agents vs Traditional Tools
How AI agents differ from existing SOC technologies
AI SOC Agent vs SIEM
Centralizes logs, enables search using predefined rules
Applies reasoning and contextual analysis to reduce false positives
AI SOC Agent vs SOAR
Automates predefined playbooks, requires manual maintenance
Adapts dynamically to novel threats without constant rule updates
AI SOC Agent vs MDR
Outsourced human analysis with latency and recurring costs
Continuous internal investigation that scales with alert volume
Core Architecture Components
The building blocks of an AI SOC agent
Data Layer
Aggregates and normalizes telemetry from endpoints, networks, cloud, identity, and threat intel
Reasoning Engine
Applies ML, statistical inference, and contextual logic to assess risk and confidence
Alert Prioritization
Scores alerts based on severity, likelihood, and business impact
Response Orchestration
Integrates with security controls for containment, enrichment, or escalation
Feedback Loop
Incorporates analyst feedback and outcomes to continuously improve accuracy
Problems AI SOC Agents Are Designed to Solve
Alert Fatigue
Reducing noise improves analyst focus and lowers burnout risk. Organizations that deploy intelligent alert triage consistently report material improvements in analyst satisfaction and productivity.
Mean Time to Respond
By automating investigation and evidence gathering, AI SOC agents shorten response cycles and reduce attacker dwell time.
SOC Staffing Constraints
AI SOC agents enable teams to scale operations without proportional increases in headcount.
Operational Scalability
As environments grow more complex, AI SOC agents scale computationally rather than organizationally.
Common Use Cases
How different organizations leverage AI SOC agents
Enterprise Security Operations
Manage high alert volumes across hybrid and cloud environments at scale
Managed Security Providers
Standardize investigations and improve analyst efficiency across client environments
Mid-Market SOC Teams
Achieve enterprise-grade outcomes with resource-constrained teams
Emerging Security Teams
Establish operational maturity without building large traditional SOCs
Frequently Asked Questions
Do AI SOC agents replace human analysts?
No. AI SOC agents augment human analysts by automating repetitive tasks and surfacing high-confidence insights. Human oversight remains essential.
Are AI SOC agents fully autonomous?
Deployment models vary. Many organizations require analyst approval before automated response actions.
Do AI SOC agents require extensive training data?
Most modern AI SOC agents are designed to work effectively with standard enterprise telemetry and improve over time through feedback.
Conclusion
AI SOC agents represent a significant evolution in security operations. By combining contextual reasoning, adaptive learning, and automation, they help SOC teams manage alert volumes, reduce noise, and respond to threats faster and more consistently.
Industry data consistently shows that organizations that reduce alert noise, automate investigation, and accelerate response experience lower breach impact, faster containment, and improved SOC resilience.
Understanding what AI SOC agents are and how they work is essential for security leaders evaluating how to modernize operations, address talent shortages, and defend against increasingly automated adversaries.